An AI Safety and Research Company
Anthropic is an AI safety and research company building Claude, a family of frontier large language models focused on being helpful, honest, and reliable. As an official Anthropic partner, Vorro built the internal expertise to work with Claude at a production level — our engineering team completed Anthropic’s Claude-certified engineer program, a requirement Anthropic sets before granting official partner status.
What This Partnership Means
Official Partner
Vorro is recognized by Anthropic as an official partner, meeting Anthropic's requirements for technology partners building on Claude.
Claude-Certified Team
Vorro's engineering team completed Anthropic's Claude-certified engineer program — a prerequisite Anthropic requires before granting official partner status.
AI Safety First
Anthropic builds safety into the model. Vorro builds it into the system around the model. A safe model alone doesn't stop prompt injection. Architecture does.
Claude-Powered Features
Claude reasons across BridgeGate’s EMR and integration data to automate connector workflows, and powers AI Associate’s clinical and administrative assistance — both built on the same permission-aware, action-gated architecture.
Secure by Design, Not by Prompt
Healthcare AI can’t depend on a model behaving well. Every Claude-powered feature in Vorro puts its security in the architecture, not in a prompt or a filter.
Controls are built in
Content from an untrusted source can't trigger a privileged action, even if no scanner catches it.
Access is checked in the query
Permissions are applied when data is fetched. A record a user can’t see is never pulled, so it never reaches Claude.
The server decides, not the model
Approvals and permissions come from parts of the system that Claude and the browser can’t influence.
We show it, not just claim it
Every control is tied to a test, a log, or a document your security team can review.
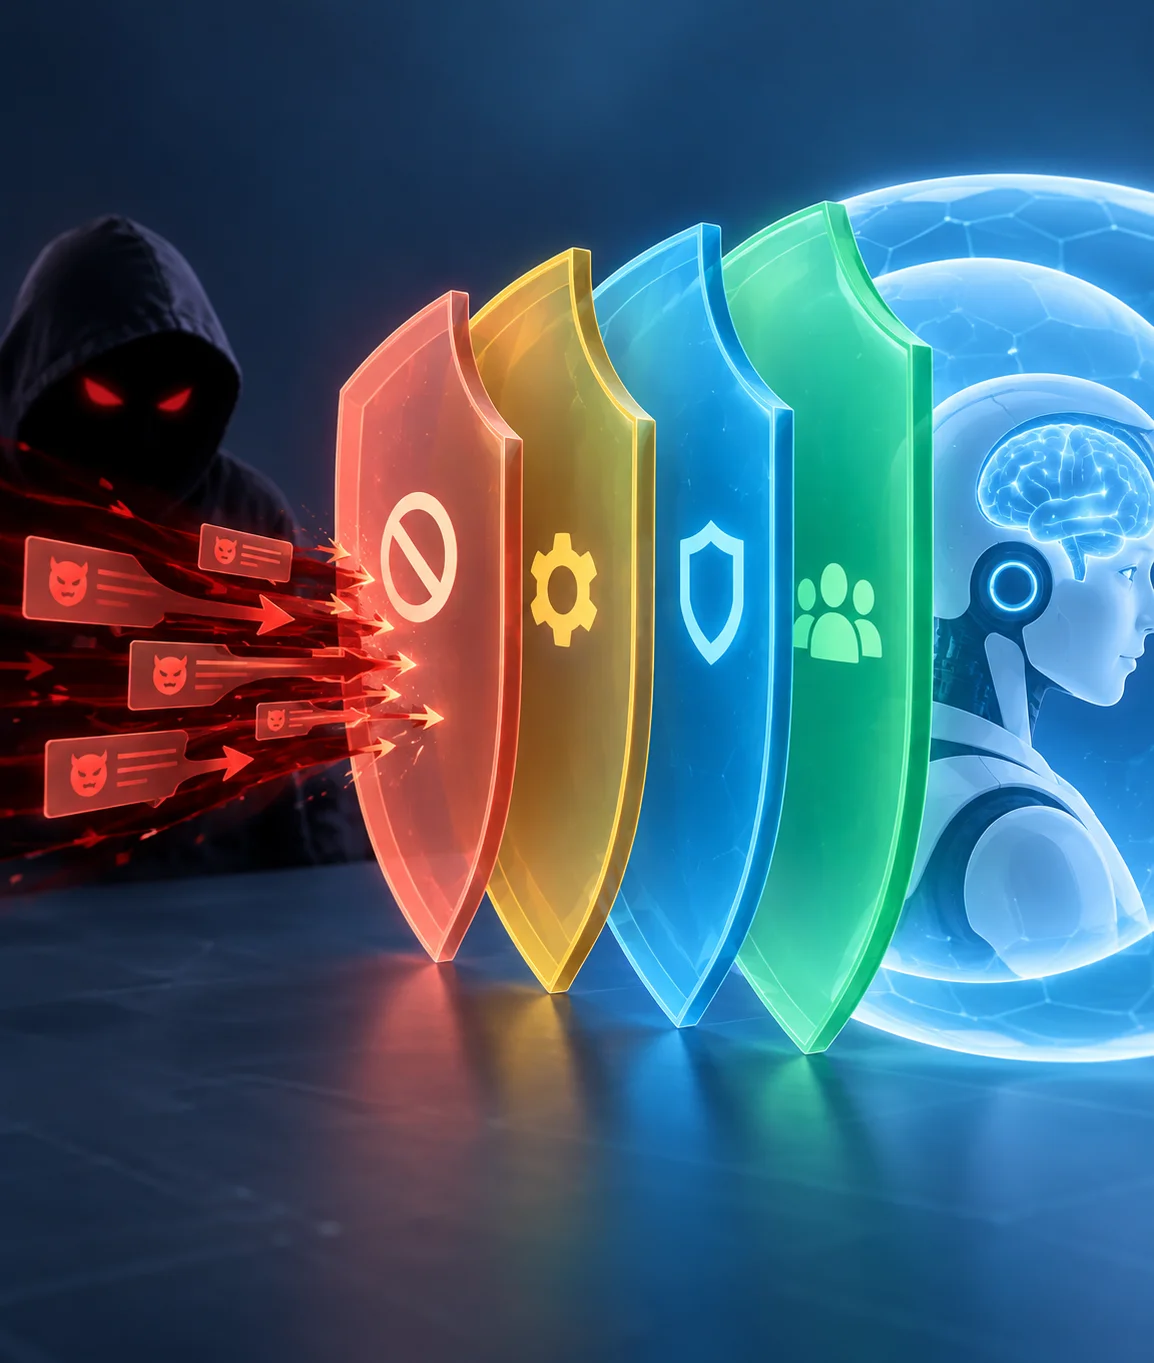
Four Layers Against Prompt Injection
Isolate
Content from documents, EMR messages, and connectors is fenced off and labeled as data, never as instructions.
Detect
New content is scanned and scored before it's indexed, and the score stays with it when it's retrieved later.
Gate every action
If a turn touched untrusted content, any action with side effects needs a one-time approval from the server, tied to the user, tool, and inputs. Claude can’t approve itself, and automations stop instead of guessing.
Monitor
Responses from the web, APIs, and tools are scanned as they arrive. Blocked actions raise security alerts for an admin to review.
Your Data, Your Boundary
Self-Hosted or Single-Tenant
Nothing is ingested until an admin turns on each source.
Inherited EMR Permissions
Permissions carry over from the EMR and other source systems, so AI never gets wider access than the user already has.
Encrypted End-to-End
Data is encrypted in transit and at rest. Credentials get extra field-level encryption, and the app won't start without its encryption key.
Full Action Audit Log
Every action the AI takes is logged with the user, session, and turn, and admins can review the log in the UI. Outbound messages are drafted for a person to send, not sent automatically.
Scoped Tool Allowlists
Each agent has its own tool allowlist, and any citation that doesn’t point to a real source is dropped.
Security & Data FAQ
Does our PHI go to Anthropic?
Yes — only the specific fields your access controls already allow for that request, never a broader data set, and it’s covered by a Business Associate Agreement (BAA) between Vorro and Anthropic.
Can Claude take an action on its own?
No. Every action with a side effect — updating a record, sending a message, triggering a workflow — requires a one-time, server-side approval that Claude cannot grant itself.
Can the AI see data a user isn’t permitted to see?
No. Permissions are enforced inside the database query itself, so a record the user can’t see is never fetched — meaning it never reaches Claude in the first place.
Is our data used to train models?
Per Anthropic’s current commercial API terms, no — data sent through the API is not used to train their models. See anthropic.com for the current terms.
Can we audit what the AI did?
Yes. Every AI action is logged with the user, session, and turn, and your admins can review that log directly in the Vorro UI.
How is it tested?
With injection test cases that use canary markers, third-party penetration testing, a software bill of materials, and vulnerability scans on every change.